

NIS2 October 2026: Countdown to ACN Inspections
For many organisations in the first cohort, the deadline for implementing baseline security measures is approaching. Here is the evidence that may be subject to verification.
31 October 2026 is not just another deadline: it marks ACN’s transition from the guidance and implementation-support phase to actual inspection and enforcement activities within the NIS2 framework.
What exactly is due.
For entities included in the national NIS list in 2025, the deadline for implementing baseline security measures is set at eighteen months from receipt of the notification confirming their inclusion, a deadline that, for the first cohort of entities, falls largely in October 2026.
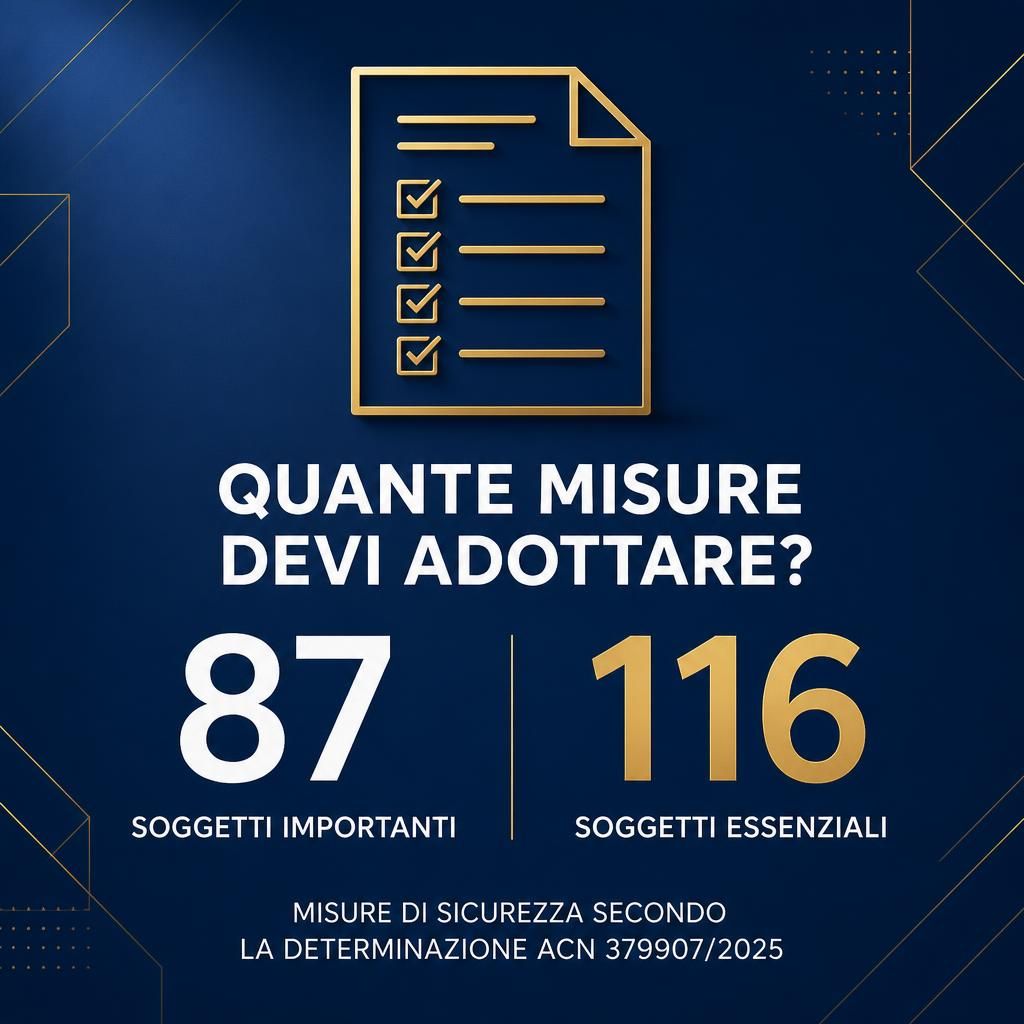
The measures are structured into functions, categories and requirements under ACN Determination No. 379907/2025: 87 requirements for important entities and 116 for essential entities.
What changes from 31 October.
From that date, the Agency may begin verification activities. The supervisory regime is not the same for all entities: essential entities are subject to
ex ante supervision, meaning proactive controls, while important entities are primarily subject to
ex post supervision, typically triggered by an unreported incident or a report from a third party.
The penalties are significant.
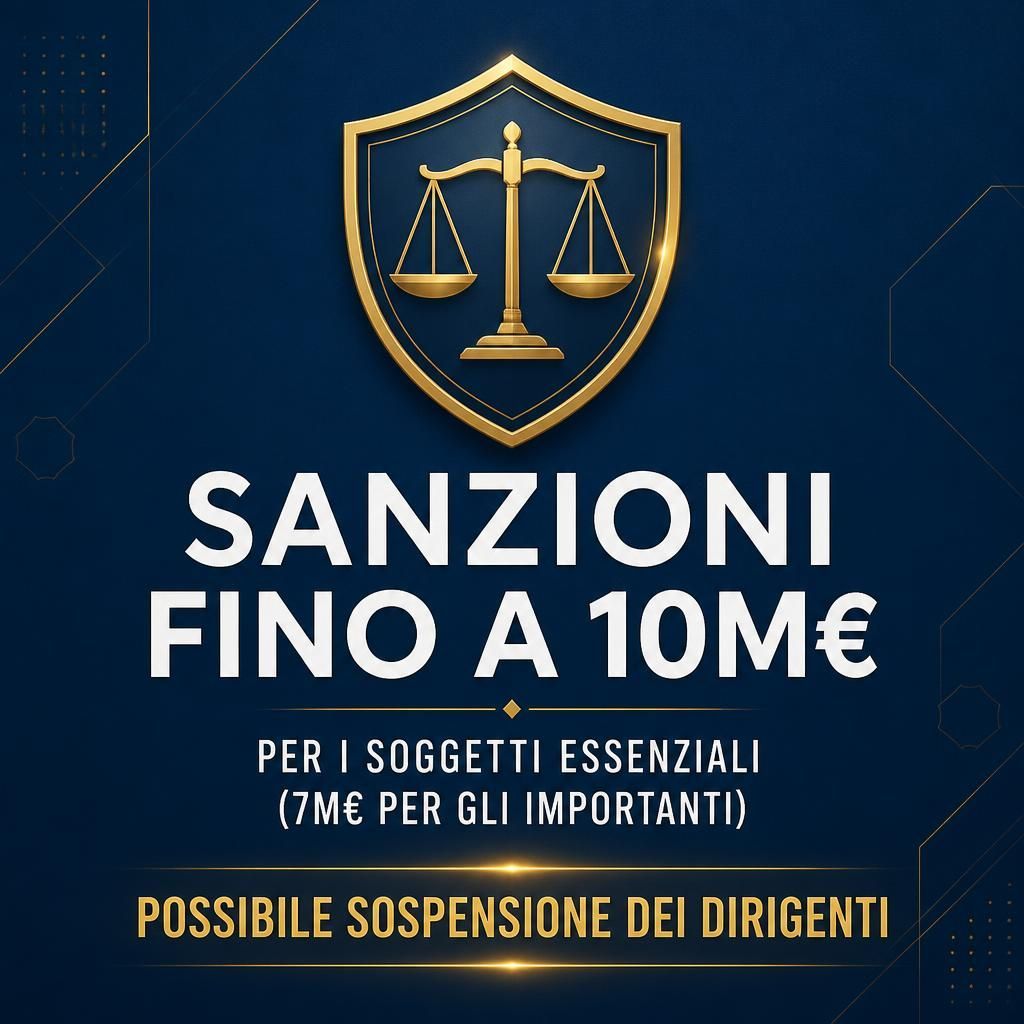
Fines can reach €10 million for essential entities and €7 million for important entities,
with an unprecedented element in the European cybersecurity framework: responsible executives may be temporarily suspended from their duties in cases of serious and repeated infringements.
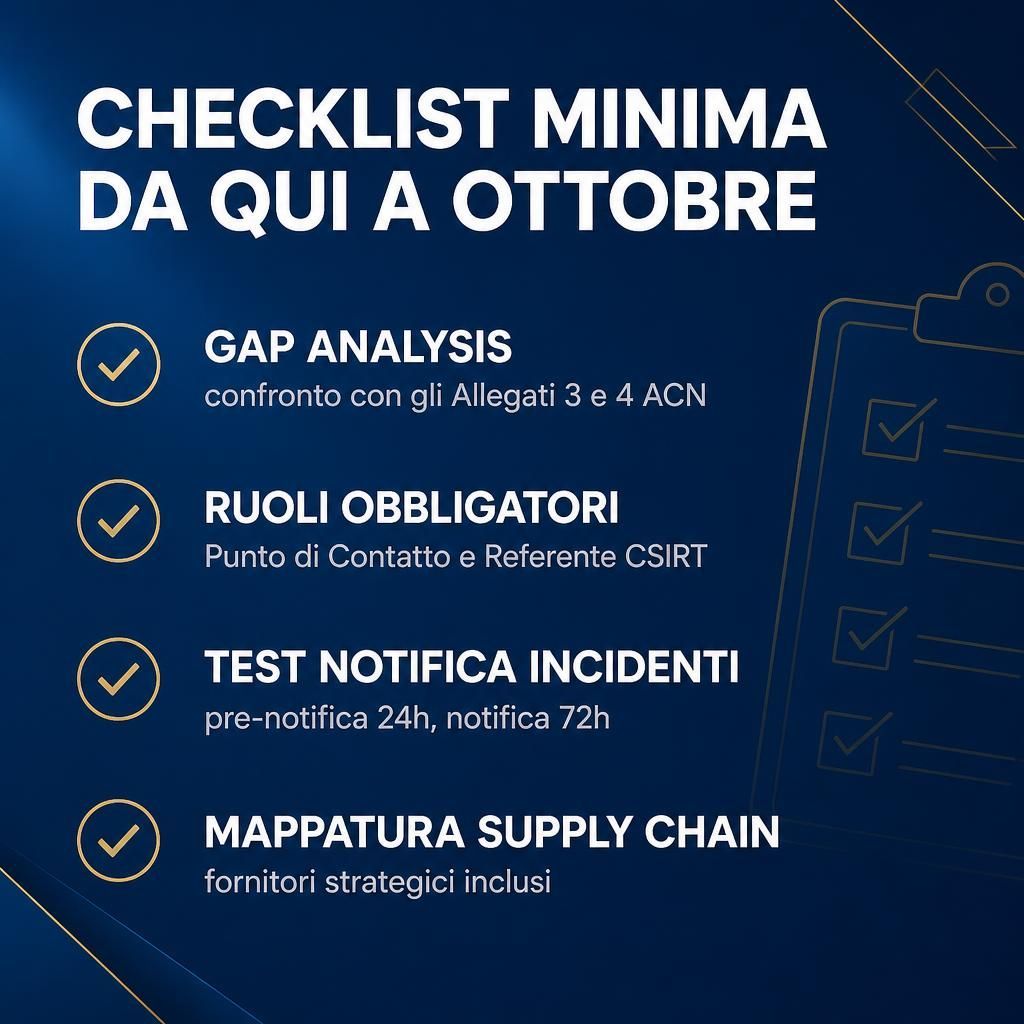
What to do, the minimum checklist:
→ Conduct a gap analysis against Annexes 3 and 4 of the ACN Determination, covering the security measures applicable to your organisation’s profile.
→ Verify mandatory roles: Point of Contact and CSIRT Contact Person, including their respective deputies.
→ Test the incident notification process (24-hour early warning, 72-hour incident notification, final report within 30 days), this obligation has already been in force since 15 January 2026.
→ Map the supply chain: review supply-chain risk management, with particular attention to direct suppliers and critical services.
Two months may sound like plenty of time. For a thorough gap analysis, it often isn’t.
Sources: Legislative Decree No. 138/2024; ACN Determination No. 379907/2025; ACN portal - “Modalità e specifiche di base” section
#NIS2 #CyberSecurity #ACN #Compliance #GRC #CyberRisk #RiskManagement #MagisPartners